OPEN SOURCE SECURITY
Not every open-source package
deserves your trust.
PexLens identifies malicious, suspicious and vulnerable open-source components — and states the signals behind each verdict, so an engineer can check the reasoning instead of taking a score on faith.
Request a Demo- Three verdict classes — malicious, suspicious, vulnerable
- Signals, not scores alone — every verdict is explained
- Judged per version — not per package name
THREE CLASSES, THREE RESPONSES
"Vulnerable" and "malicious"
are not the same problem.
A vulnerable component is honest code with a known flaw. A malicious one was published to do harm. Treating both as a single number is why security backlogs stall — so PexLens separates them, and says which it found.
MALICIOUS
Published to do harm
Credential theft, hidden payloads, typosquatted names, install-time execution. There is no safe version to upgrade to — the package itself is the attack.
Response: remove it and find everywhere it reached.
SUSPICIOUS
Not proven, not clean
Abrupt maintainer changes, unexplained behaviour shifts, obfuscated code, releases that do not match their repository. Enough to warrant a look before it spreads.
Response: remove it and find everywhere it reached.
VULNERABLE
Known flaw, known fix
Most organizations cannot say which packages or extensions are on which developer machine today.A published CVE affects the version in use. The finding carries the identifier, the severity and the release that resolves it where one exists.
Response: remove it and find everywhere it reached.
WHAT WE LOOK AT
Nine signals behind every verdict
No single signal decides anything. A verdict is the pattern across all three groups.
GROUP 01 · THE CODE
Install-time execution
Scripts that run before any code is imported
Credential and key access
Read of token, cloud and SSH paths a library has no reason to touch
Obfuscation and payloads
Encoded blobs, dynamic evaluation, code that unpacks itself at runtime
GROUP 02 · THE PUBLISHER
Maintainer change
Ownership handed over, then a release soon after.
Release irregularity
A dormant package publishing again, or versions arriving out of pattern.
Source mismatch
Published artifact does not correspond to the public repository it claims.
GROUP 03 · THE IDENTITY
Name similarity
Typosquats and near-misses on widely used package names.
Known advisories
CVE and advisory data matched against the exact version resolved.
Reach and adoption
Analyze download velocity trends, dependent chains, and historical reputation of critical code modules.
VERSION-LEVEL TRUTH
The package is fine. The version is not.
Most open-source risk arrives in a single release of an otherwise reputable package. A verdict attached to a package name is useless; PexLens judges the exact version resolved, and tells you which release is clean.
Findings are pinned to the version in use, not the latest published
Where a fixed release exists, the finding names it
A cleared version stays cleared — the judgement is not re-litigated per team
IN THE CONSOLE
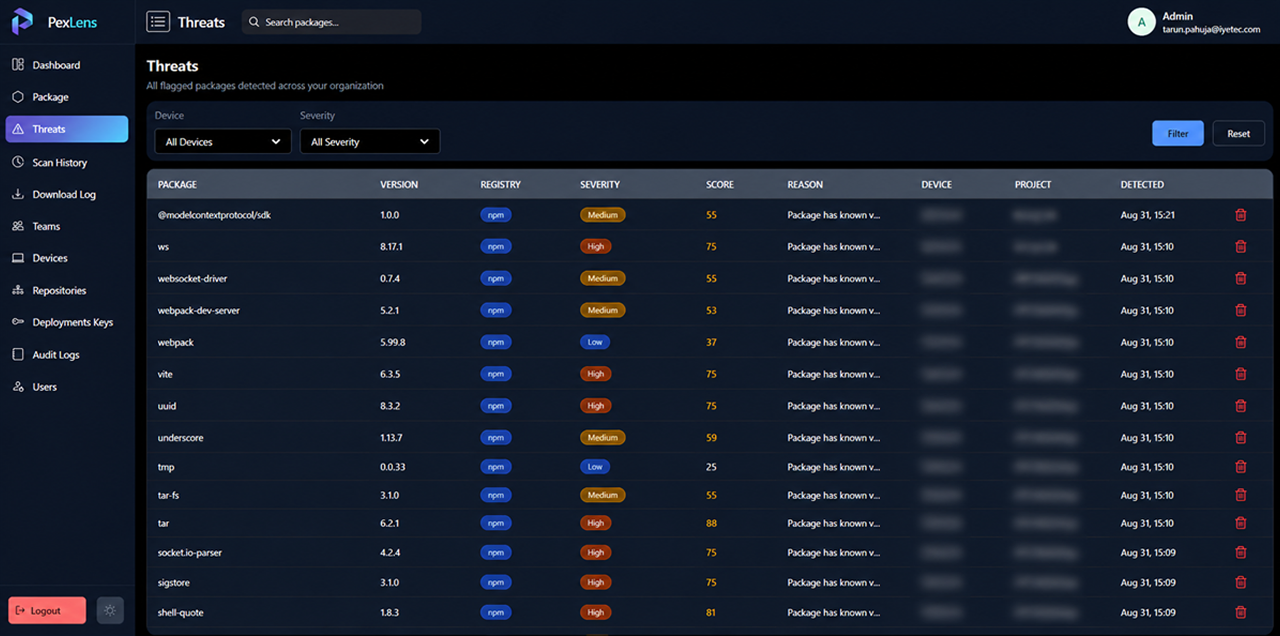
Every flagged component, with its reason
Package, version, registry, severity, score and the reason it was flagged — the same verdict language used everywhere else in PexLens.
Filter by severity
Sort by score
What we cover
The Ecosystems we judge
START WITH AN INVENTORY
Make every package request a security decisions.
Pexlens helps you secure open source at every step of the supply chain.
FAQ
Open source security: common questions
What is open source security?
Open source security means making sure the open-source packages your software depends on are not malicious, compromised or dangerously vulnerable.
How is a malicious package different from a vulnerable one?
A vulnerable package has an accidental flaw, usually tracked as a CVE. A malicious package was built or modified to cause harm, for example to steal credentials. PexLens detects both.
Does PexLens include vulnerability (CVE) intelligence?
Yes. Vulnerability intelligence is included on every plan, and policies can set CVE and risk thresholds alongside malicious-package detection.
How is PexLens different from a traditional vulnerability scanner?
Vulnerability scanners and SCA tools mainly match your dependencies against known CVEs. PexLens also looks for malicious intent and risky change in packages and extensions, such as credential theft, suspicious updates or publisher changes, and can block them at install time, before the code runs.
What is a software supply chain attack?
A supply chain attack compromises something you trust instead of attacking you directly, for example a malicious package published to npm or PyPI, a hijacked maintainer account or a poisoned update. The malicious code then reaches every team that installs it.
Which package ecosystems are supported?
PexLens analyzes major open-source package ecosystems, including npm, PyPI, Maven and RubyGems, along with browser and IDE extensions. Support for additional ecosystems is expanding as the platform grows.
Related