Opens in a new tab
PexLens logo
PexLens logo
Pricing
Add your offcanvas content in here

SUPPLY CHAIN ECOSYSTEM SECURITY

Secure Your Supply Chain. Strengthen Your Business.​

PexLens helps organizations identify, assess, and manage risks across their supply-chain ecosystem.​

How PexLens Works

SCAN

Scan endpoints for packages & browser extensions
COLLECT

Send inventory to PexLens Brain securely

ANALYZE

Analyze against 80M+ packages & behavior patterns

SCORE

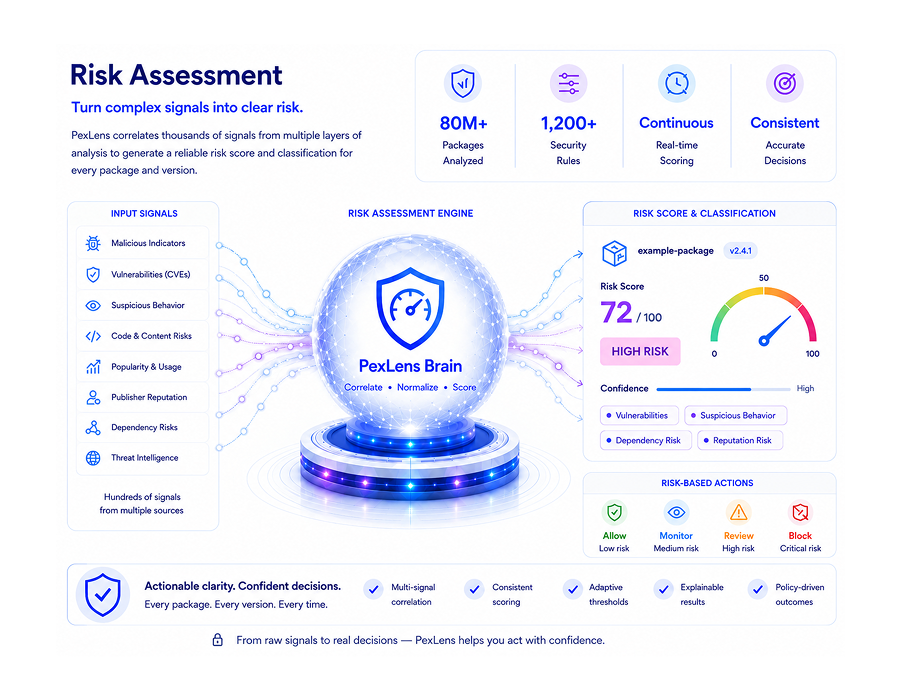
Score for risk, malware, suspicious behavior & reliability

PROTECT

Block threats. Enforce policies. Keep your organization safe

Software Supply Chain Security
Real-time Protection
Malware & Risk Detection
Policy-driven Control
Continuous Intelligence
Enterprise Ready

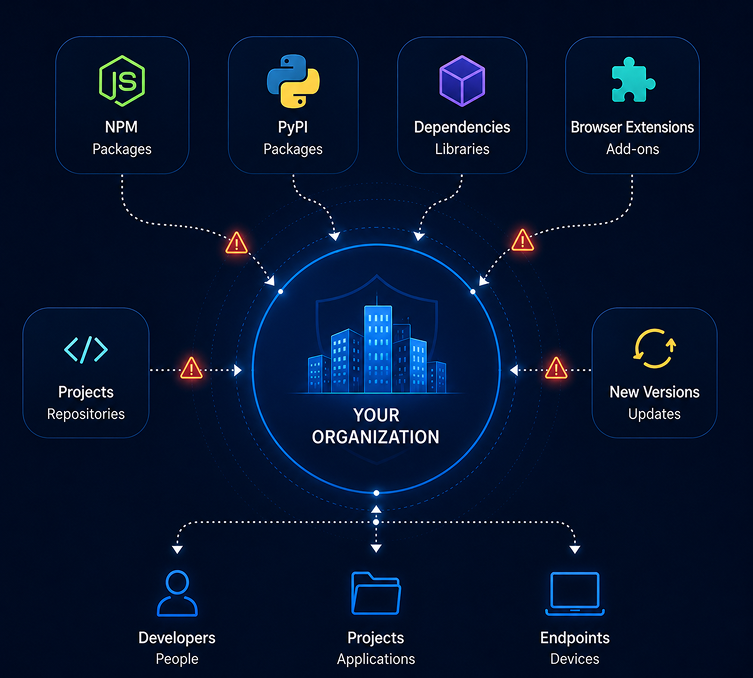
THE SOFTWARE SUPPLY CHAIN

Every package, dependency and browser extension can become an entry point.

Modern organizations rely on thousands of software components that change every day. Without visibility and control, a single compromised or vulnerable component can introduce risk into the organization.

Your software ecosystem is constantly changing.
Do you know what you're allowing in?

Every package, dependency and browser extension can become an entry point: PexLens supply chain security illustration

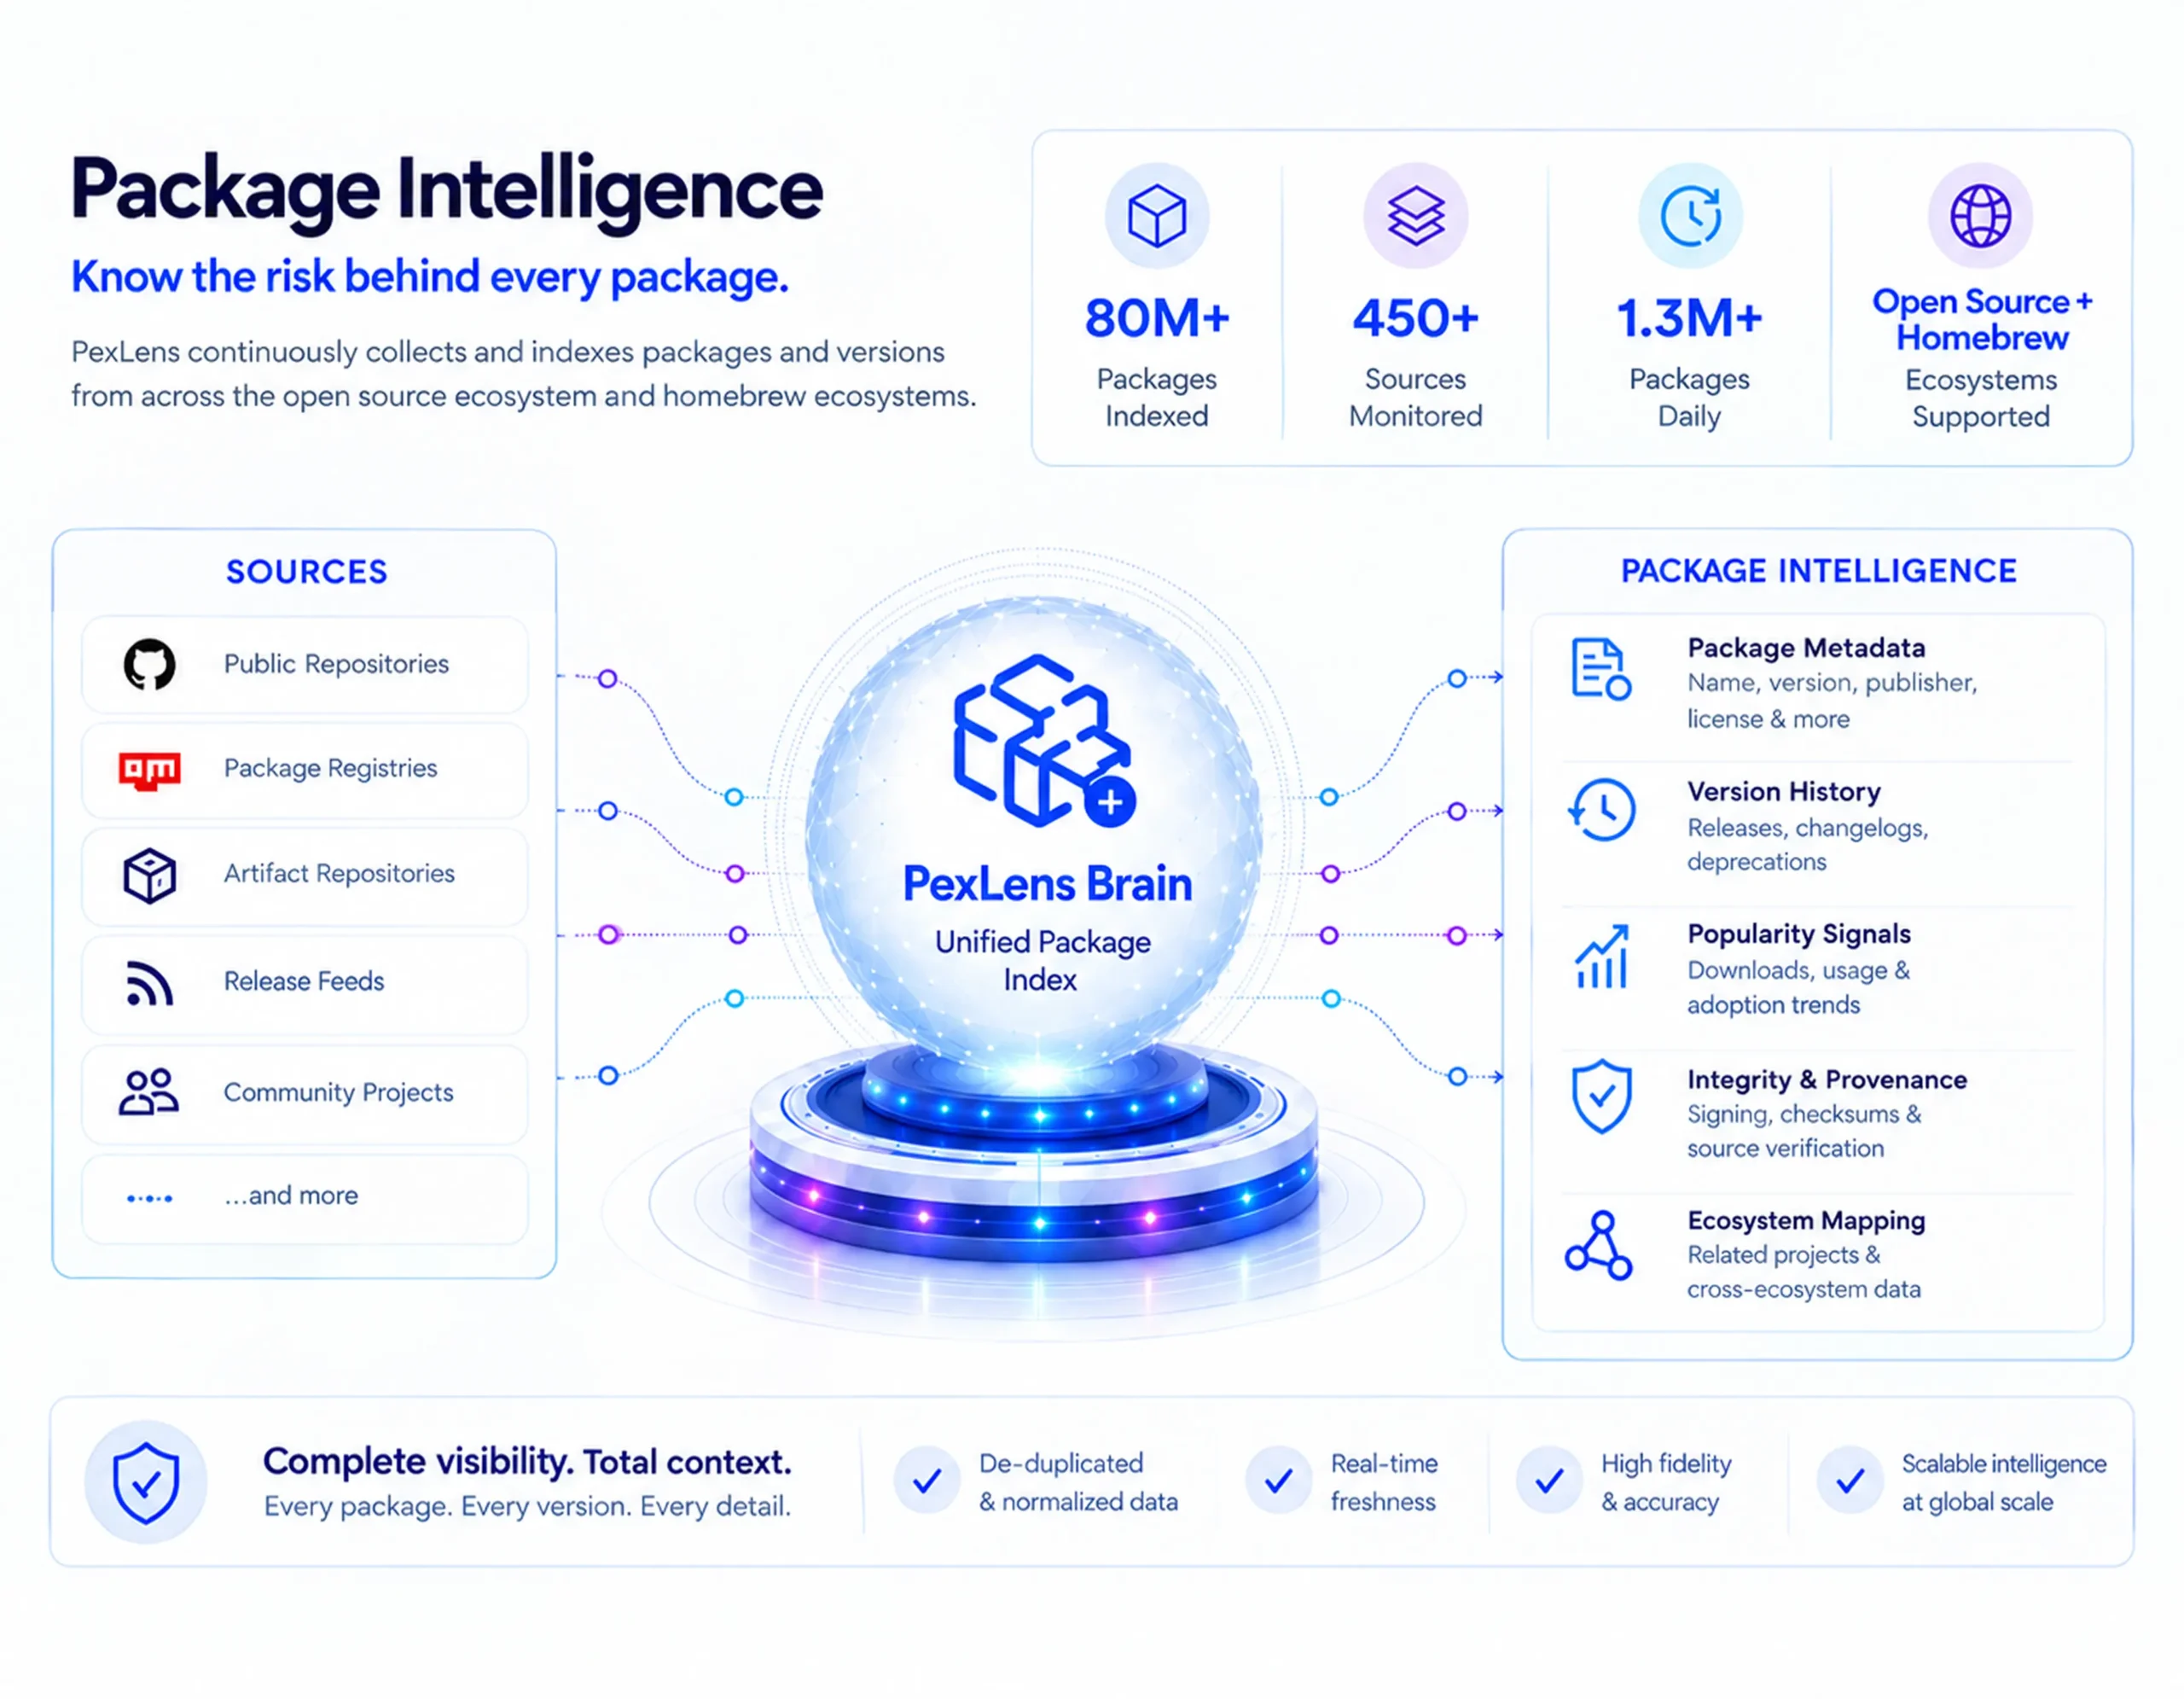
THE PEXLENS BRAIN

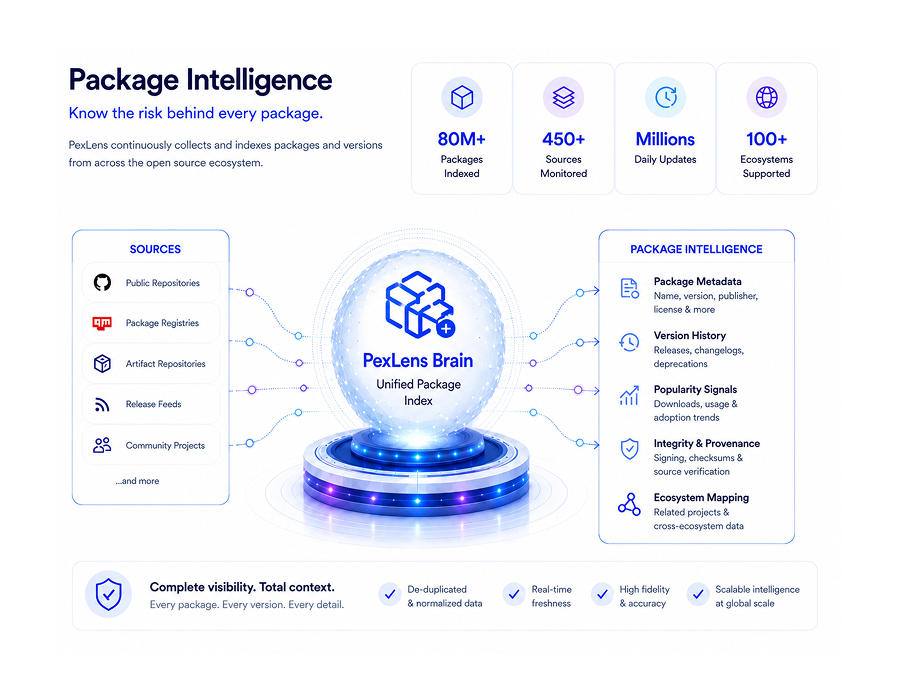
Intelligence behind every package and extension 
The PexLens brain: PexLens supply chain security illustration

REAL-TIME PROTECTION

Stop threats before they reach your endpoints​
PexLens evaluates package requests in real time and applies your organization's security policies ​ before software is installed​

The decision engine

Policy-driven decisions​
Apply your own security thresholds to every package request​

From detection to action

Protection doesn't stop at detection​
When PexLens identifies a threat, your organization can ​respond immediately -with automated blocking, real-time notifications​and administrator-led remediation​

REAL-TIME PROTECTION

Stop threats before they reach your endpoints​
PexLens evaluates package requests in real time and applies your organization's security policies ​ before software is installed​

The decision engine

Policy-driven decisions​
Apply your own security thresholds to every package request​

From detection to action

Protection doesn't stop at detection​
When PexLens identifies a threat, your organization can ​respond immediately -with automated blocking, real-time notifications​and administrator-led remediation​

What PexLens Protects Against​

Protect Against the Risks Hidden in Your Software Supply Chain​

Malicious Packages

Stop packages containing malicious code.

Vulnerable Components

Enforce your organization’s CVE thresholds.

Compromised Dependencies

Identify compromised or suspicious components.

Supply-Chain Attacks

Detect threats before they reach endpoints.

Malicious Extensions

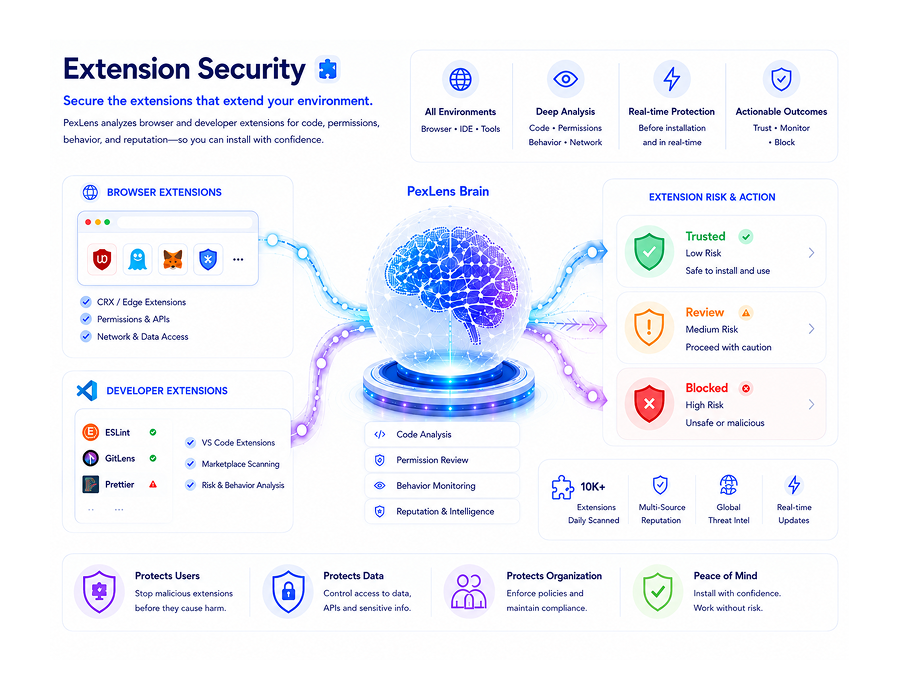
Assess browser and developer extensions.

Policy Violations

Prevent software that violates organizational security policies.

See Your Software Supply Chain Clearly

Discover packages, dependencies, extensions, threats and affected endpoints from one place.​

Built for the Teams Responsible for Security

Security Leadership

Understand your software supply-chain exposure and enforce organizational risk policies.

Application Security / DevSecOps

Assess packages, dependencies and extensions before they introduce risk.

IT & Endpoint Security

Discover software across endpoints and respond to threats quickly.
From Detection to Action: PexLens supply chain security illustration

From Detection to Action​

Know What Enters Your Organization. Control What Stays​
PexLens brings software supply-chain intelligence, real-time protection ​ and policy enforcement into one platform​

FROM REQUEST TO VERDICT

One package. Multiple security signals.

From request to verdict: PexLens software supply chain security illustration

Package Information

Name, version, registry and metadata
From request to verdict: PexLens software supply chain security illustration

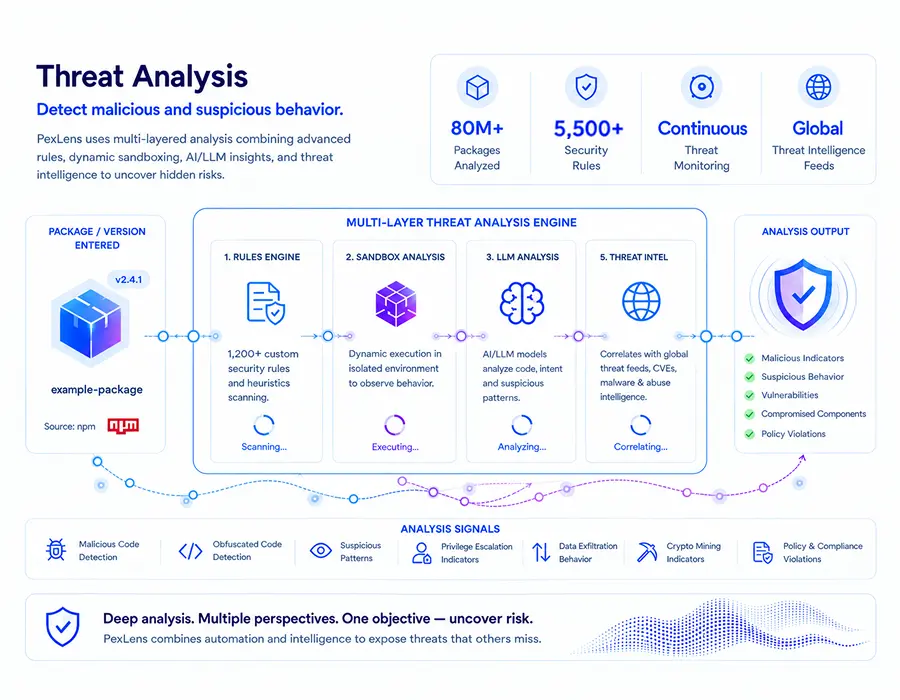
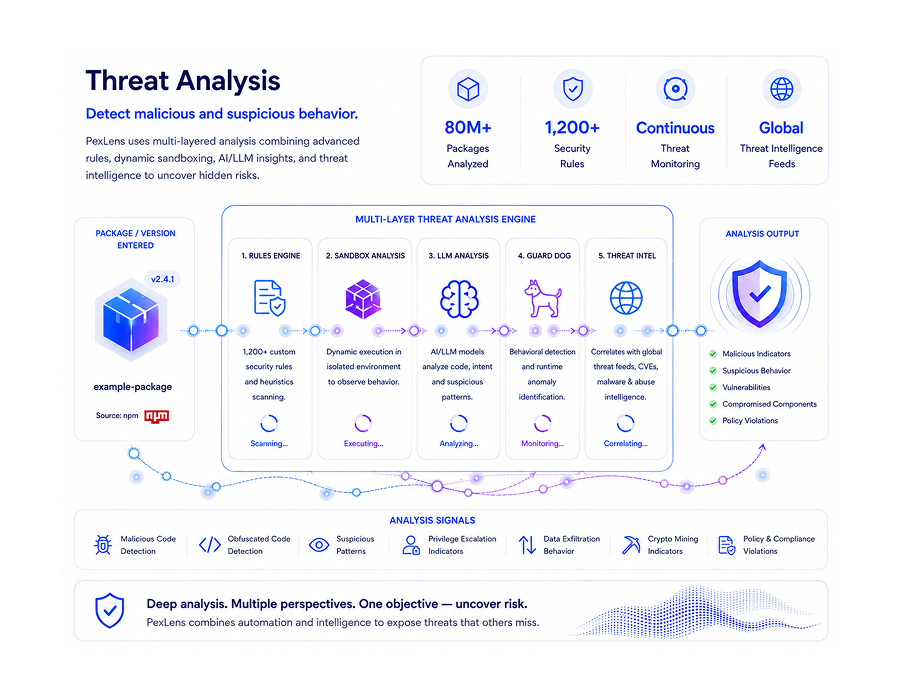
Threat Analysis

Malicious code, suspicious behavior, indicators
From request to verdict: PexLens software supply chain security illustration

Dependency Analysis

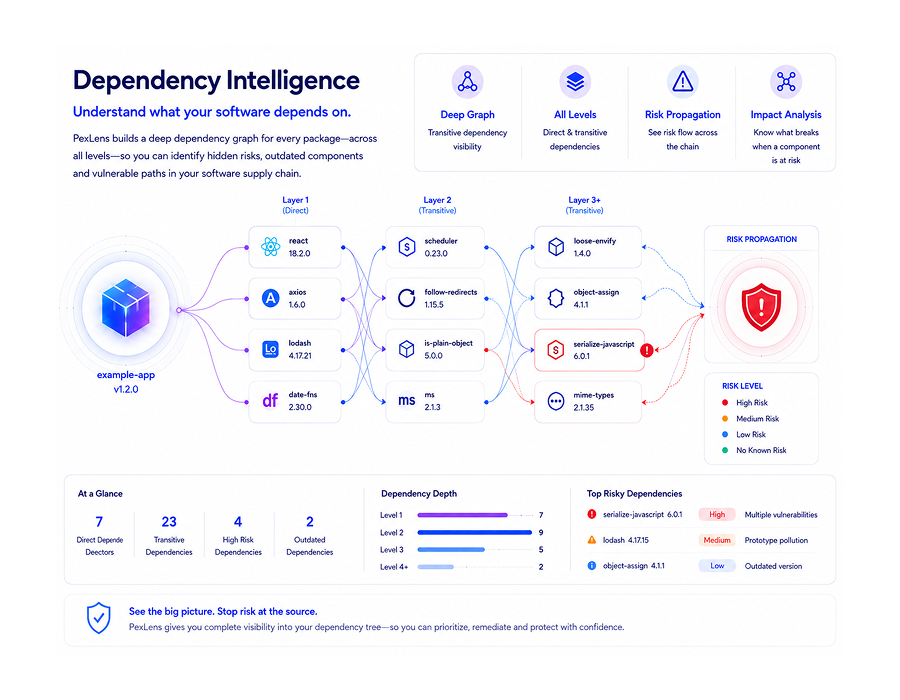
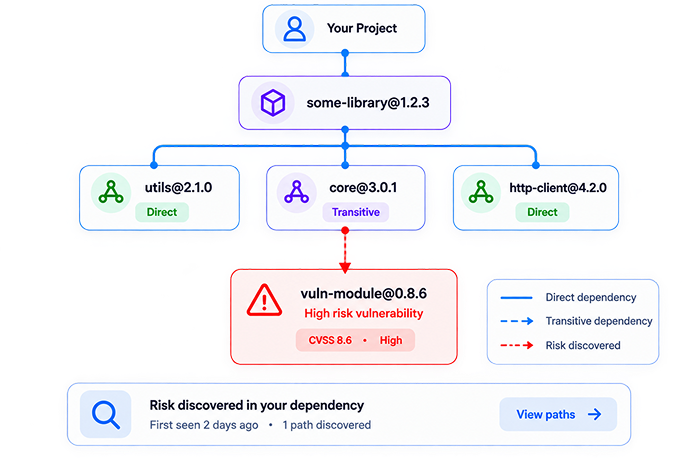
Direct & transitive dependencies
From request to verdict: PexLens software supply chain security illustration

Vulnerability Analysis

Known CVEs and security weaknesses
From request to verdict: PexLens software supply chain security illustration

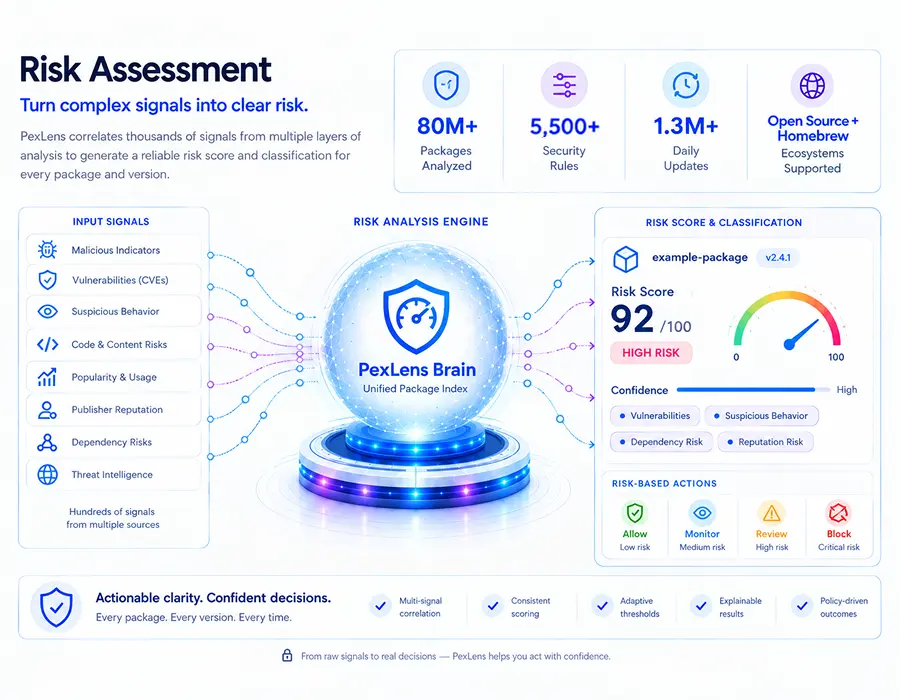
Risk Assessment

Combined signals produce a risk score
From request to verdict: PexLens software supply chain security illustration

Policy Decision

Allow, review or block

PexLens evaluates multiple signals together so you can make confident decisions, not guesses.

SECURITY CONTEXT & DECISION

Understand the risks. Make the right decision.

PexLens analyzes the dependency path, evaluates security signals, and helps you enforce the right policy with confidence.
RISK SCORE
HIGH RISK
0/100
Threat level: High
What does this mean?
Security context & decision: PexLens software supply chain security illustration

08 VISIBILITY & AUDIT TRAIL

Every decision. Every time.

Maintain complete visibility with detailed logs and audit trails for your security and compliance needs.
Scan History
View all
DEVICE
LAST SCAN
THREATS
Zeenat-PC
Aug 28, 14:51
3
Build-Server-01
Aug 28, 14:16
1
Alice-MacBook
Aug 27, 16:43
0
Real-time scan visibility
Download Log
View all
PACKAGE
VERSION
STATUS
package x
4.17.21
Blocked
express
4.18.2
Allowed
package x
0.7.1
Blocked
Track all package download attempts
Audit Logs
View all
EVENT
DEVICE
SEVERITY
Package blocked
Zeenat-PC
High
Policy updated
Admin
Medium
Scan completed
Zeenat-PC
Low
Comprehensive audit trail

FAQ

Answers to common questions about how PexLens protects your software supply chain.
What is a software supply chain attack?

A supply chain attack compromises something you trust instead of attacking you directly, for example a malicious package published to npm or PyPI, a hijacked maintainer account or a poisoned update. The malicious code then reaches every team that installs it.

What does PexLens scan?

PexLens scans software packages installed on endpoints as well as packages present within project folders. It also identifies browser and developer extensions, giving organizations visibility into the software components running across their environment.

Which package ecosystems are supported?

PexLens analyzes major open-source package ecosystems, including npm, PyPI, Maven and RubyGems, along with browser and IDE extensions. Support for additional ecosystems is expanding as the platform grows.

How does PexLens block malicious packages?

Package installation requests can be routed through the PexLens Proxy, where the package is evaluated against PexLens intelligence and your organization’s security policies. Packages that fail the defined security criteria can be blocked before installation.

Can organizations define their own security policies?

Yes. Organizations can define their own security requirements, including risk and CVE thresholds, and PexLens applies those policies when evaluating package requests.

Does PexLens monitor browser and developer extensions?

Yes. PexLens can identify and assess browser extensions and developer-environment extensions, including VS Code extensions, helping organizations detect malicious, suspicious, or risky extensions.

How does PexLens handle newly published packages?

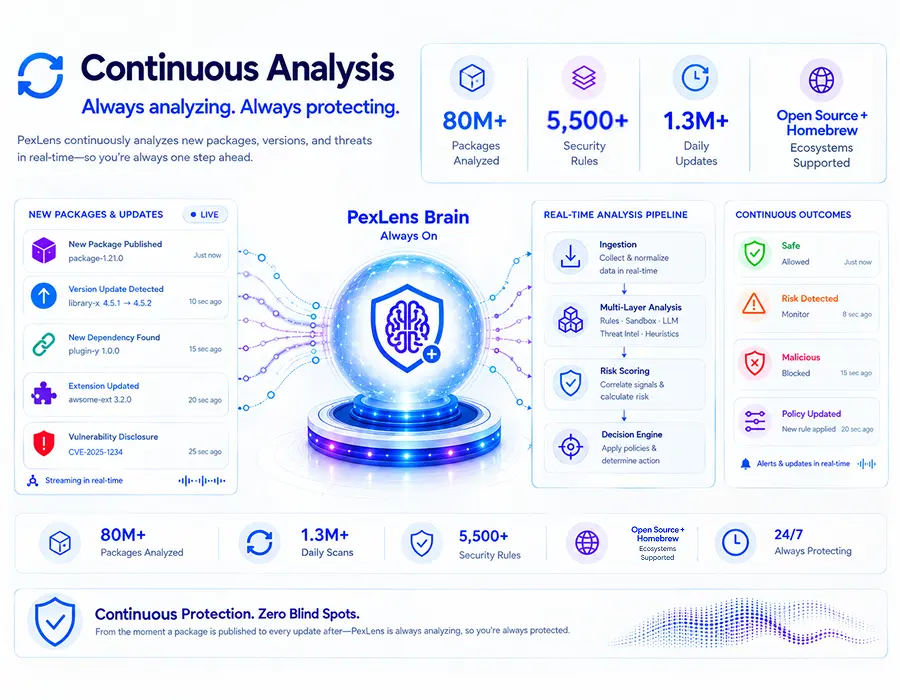
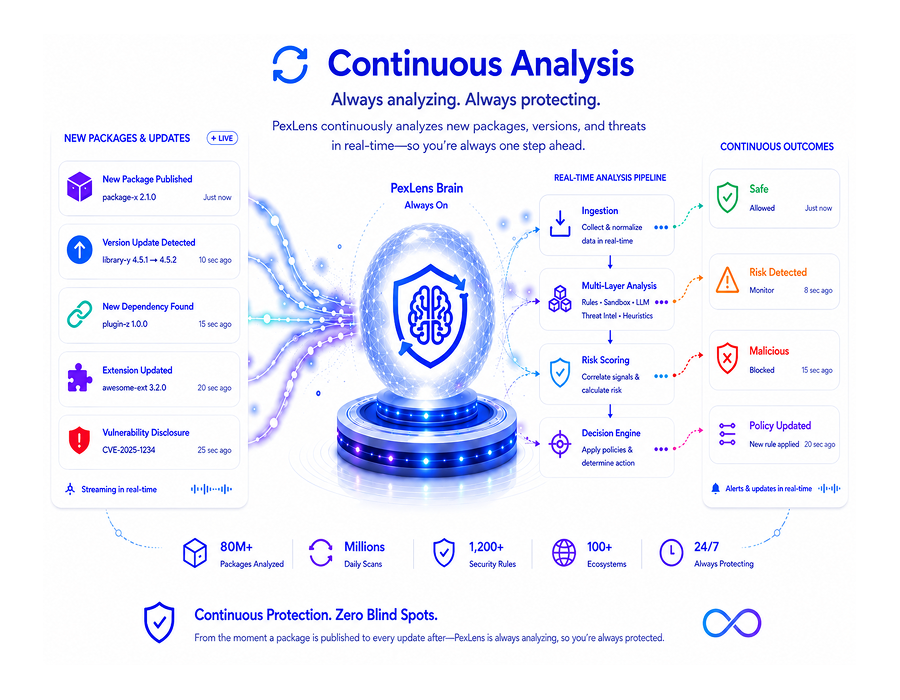
PexLens continuously discovers and analyzes new packages and package versions, updating its intelligence as the software ecosystem evolves. This helps organizations make decisions using current risk information rather than relying only on historical scans.

How is PexLens different from a traditional vulnerability scanner?

Vulnerability scanners and SCA tools mainly match your dependencies against known CVEs. PexLens also looks for malicious intent and risky change in packages and extensions, such as credential theft, suspicious updates or publisher changes, and can block them at install time, before the code runs.

Can PexLens protect private/internal packages?

Yes. Using advanced hashes, PexLens maps internal binaries without leaking proprietary raw source code to external servers.

View all FAQs →