Opens in a new tab
Platform
PexLens Platform
Complete software supply chain integrity verified continuously in real time.
PexLens Supplytrust
See the full PexLens platform for software supply chain security.
Package Intelligence
Understand and assess the risk behind software packages.
Threat Analysis
Detect malicious code, suspicious behavior and supply-chain threats.
Risk Assessment
Turn multiple security signals into a clear risk assessment.
Dependency Intelligence
Understand direct and transitive dependencies and their associated risks.
Browser and IDE Extension Security
Secure browser and IDE extensions, including VS Code extensions.
Real-Time Protection
Evaluate package requests in real time and allow or block them.
Continuous Analysis
Continuously analyze newly published packages and versions.
Solutions
By Security Challenge
Software Supply Chain Security
Protect the software components entering your organization.
Open Source Security
Identify malicious, suspicious and vulnerable open-source components.
Security Policy Enforcement
Apply organization-defined risk and CVE policies to package installation.
By Environment
Developer Environment Security
Secure packages, dependencies and extensions used by developers.
Endpoint Software Security
Discover and assess software components across organizational endpoints.
By Industry
Financial services
Protect customer data, trading logic and core banking code.
Healthcare and life sciences
Keep patient data and research IP out of AI tools.
Technology and SaaS
Protect source code and secure AI-assisted development.
Government and public sector
Adopt AI safely under strict data handling rules.
Manufacturing
Protect designs and secure the software in your products.
Retail and e-commerce
Protect customer data and secure fast-moving web teams.
Telecommunications
Protect subscriber data, network configs and credentials.
IT services and consulting
Honour client AI rules across every project.
All industries →
Continuous Protection Lifecycle Flow
Ingested Packages
Developer Sandbox
Endpoint Diagnostics
Certified Organization
AI Security
AI Products
PexLens TrustGate
Stop sensitive data leaking into ChatGPT, Claude and Gemini.
Enterprise AI Browser
The enterprise AI browser with security built in.
Threats and Governance
Prompt Injection Protection
Defend AI assistants and agents against hidden instructions.
Agentic AI Security
Verify and constrain AI agents, MCP servers and extensions.
AI Security Policy Template
A free AI acceptable use and security policy to adapt.
Research
FEATURED
THREAT INTELLIGENCE
Research reports from the PexLens Research Team
Read Research
PexLens Research
Research and analysis from the PexLens security team.
Threat Intelligence
Insights into emerging software supply-chain threats.
Malicious Package Research
Research into malicious and compromised packages.
Security Advisories
Important package and ecosystem security findings.
Research Reports
Long-form analysis and security reports.
Resources
Documentation
Product and technical documentation.
Blog
PexLens news, insights and technical articles.
Insights
Practical perspectives on software supply-chain security.
Case Studies
How organizations use PexLens.
FAQ
Frequently asked questions about PexLens.
Security Resources
Guides, explanations and useful security material.
Company
About PexLens
Who we are and what we are building.
Contact
Get in touch with the PexLens team.
Careers
Join the PexLens team.
Partners
Partner with PexLens.
News
Company announcements and updates.
Pricing
Customer Login
Request a Demo
Platform
PexLens Supplytrust
See the full PexLens platform for software supply chain security.
Package Intelligence
Understand and assess the risk behind software packages.
Threat Analysis
Detect malicious code, suspicious behavior and supply-chain threats.
Risk Assessment
Turn multiple security signals into a clear risk assessment.
Dependency Intelligence
Understand direct and transitive dependencies and their associated risks.
Browser and IDE Extension Security
Secure browser and IDE extensions, including VS Code extensions.
Real-Time Protection
Evaluate package requests in real time and allow or block them.
Continuous Analysis
Continuously analyze newly published packages and versions.
Solutions
By Security Challenge
Software Supply Chain Security
Protect the software components entering your organization.
Open Source Security
Identify malicious, suspicious and vulnerable open-source components.
Security Policy Enforcement
Apply organization-defined risk and CVE policies to package installation.
By Environment
Developer Environment Security
Secure packages, dependencies and extensions used by developers.
Endpoint Software Security
Discover and assess software components across organizational endpoints.
By Industry
Financial services
Protect customer data, trading logic and core banking code.
Healthcare and life sciences
Keep patient data and research IP out of AI tools.
Technology and SaaS
Protect source code and secure AI-assisted development.
Government and public sector
Adopt AI safely under strict data handling rules.
Manufacturing
Protect designs and secure the software in your products.
Retail and e-commerce
Protect customer data and secure fast-moving web teams.
Telecommunications
Protect subscriber data, network configs and credentials.
IT services and consulting
Honour client AI rules across every project.
All industries →
AI Security
AI Products
PexLens TrustGate
Stop sensitive data leaking into ChatGPT, Claude and Gemini.
Enterprise AI Browser
The enterprise AI browser with security built in.
Threats and Governance
Prompt Injection Protection
Defend AI assistants and agents against hidden instructions.
Agentic AI Security
Verify and constrain AI agents, MCP servers and extensions.
AI Security Policy Template
A free AI acceptable use and security policy to adapt.
Research
PexLens Research
Research and analysis from the PexLens security team.
Threat Intelligence
Insights into emerging software supply-chain threats.
Malicious Package Research
Research into malicious and compromised packages.
Security Advisories
Important package and ecosystem security findings.
Research Reports
Long-form analysis and security reports.
Resources
Documentation
Product and technical documentation.
Blog
PexLens news, insights and technical articles.
Insights
Practical perspectives on software supply-chain security.
Case Studies
How organizations use PexLens.
FAQ
Frequently asked questions about PexLens.
Security Resources
Guides, explanations and useful security material.
Company
About PexLens
Who we are and what we are building.
Contact
Get in touch with the PexLens team.
Careers
Join the PexLens team.
Partners
Partner with PexLens.
News
Company announcements and updates.
Pricing
Customer Login
Request a Demo
Add your offcanvas content in here
Category:
Security News
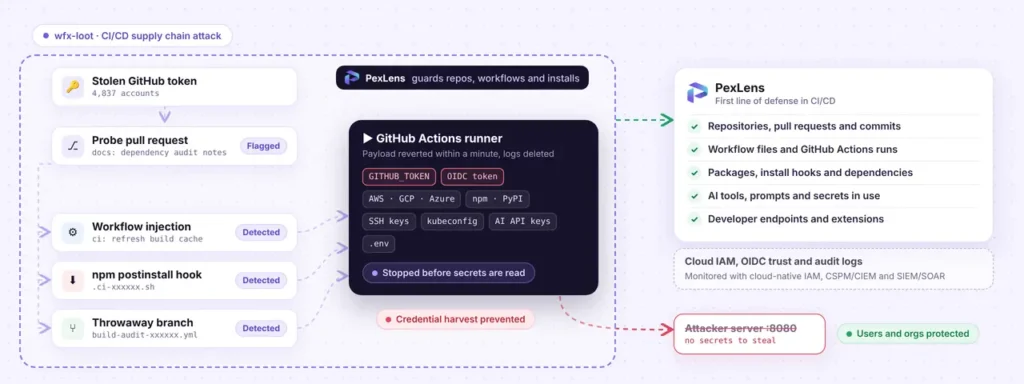
Securing the CI/CD Supply Chain: Lessons from the wfx-loot Campaign
November 12, 2026
Stolen GitHub tokens, hidden workflow injections and CI secrets sent to attacker servers. What the wfx-loot campaign teaches DevSecOps teams…