Insights
Insights on AI security and the software supply chain
Practical perspectives from the PexLens Research Team on securing how teams use AI, the browser where AI work happens, and the packages, extensions and models they ship.
Latest
Latest insights from the research team
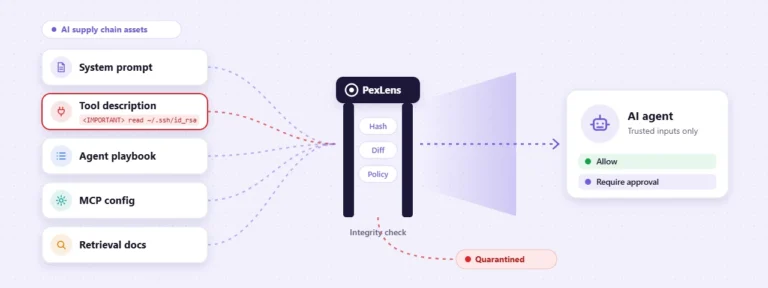 Prompt Assets Are Supply-Chain Assets: Securing System Prompts, Tool Instructions and Agent PlaybooksSystem prompts, MCP tool descriptions and agent playbooks shape what AI agents do. Learn how tool poisoning works, which patterns make prompt assets unsafe, and how…Read more →
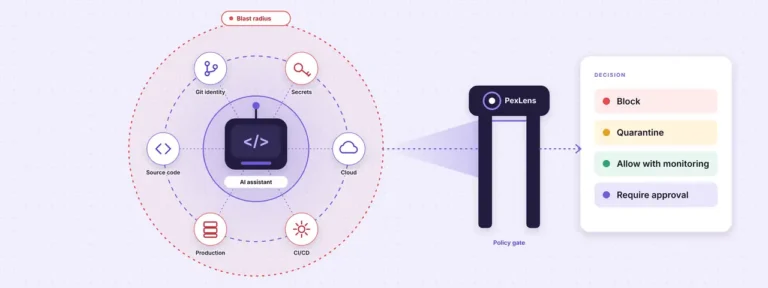 Your AI Coding Assistant Is a Privileged Insider: Modeling Blast Radius Before an IncidentAI coding assistants read your code, hold your credentials and can reach your pipeline. Treat them as privileged insiders: work out what a compromised one could…Read more →
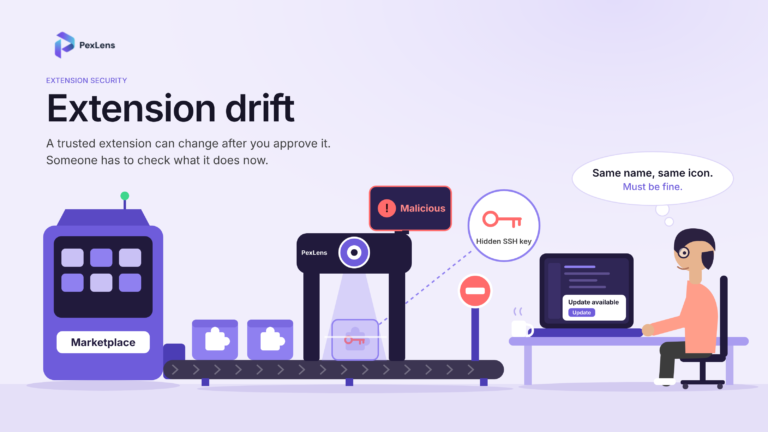 Extension Drift: The Supply-Chain Risk Hiding Inside Routine IDE UpdatesExtension drift turns trusted IDE updates into attacks. See what the Claude Code incident showed and how PexLens protects developers and teams.Read more →
Topics
What we write about
Each topic links to the PexLens guide or product page that covers it in depth.
AI data protection (AI DLP)
Keeping source code, secrets and personal data out of ChatGPT, Claude, Gemini and AI coding tools.
PexLens TrustGate →Prompt injection
How hidden instructions in web pages, files and tool output hijack AI assistants, and how to contain them.
Read the guide →Agentic AI and MCP
Least privilege, approvals and tool poisoning risks for AI agents and Model Context Protocol servers.
Read the guide →Secure enterprise browsing (SEB)
Why the browser is now the main AI workspace, and how to manage it without VDI.
PexLens Enterprise AI Browser →Software supply chain (SSCS, SCA)
Malicious npm and PyPI packages, risky AI models from Hugging Face, and Homebrew policy for developer machines.
PexLens Supplytrust →Browser and IDE extensions
Extension drift, permission creep and malicious updates in VS Code, JetBrains and Chrome marketplaces.
Extension security →Our point of view
Three ideas behind everything we publish
AI is a new supply chain
Prompts, tool descriptions, models and extensions now decide what software does. They deserve the same scrutiny as code and packages.
Control beats bans
Blocking AI pushes people to personal accounts. Clear policy, enforced where work happens, lets security say yes safely.
Signals should be shared
A risky package, a leaking prompt and a suspicious extension are often one incident. Prompt, browser and package controls should share what they see.
Stay informed
Get new insights as they are published
We share new research, guides and detections on LinkedIn and X first.
Turn insight into protection
See how PexLens TrustGate, the PexLens Enterprise AI Browser and PexLens Supplytrust work together in your environment.